Apple Issues New Warnings for Mercenary Spyware Targets, Updates Security Protocols
Following a fresh round of alerts reported by Citizen Lab, Apple clarifies that notifications indicate high-confidence targeting activity rather than confirmed data breaches, advising immediate adoption of Lockdown Mode.
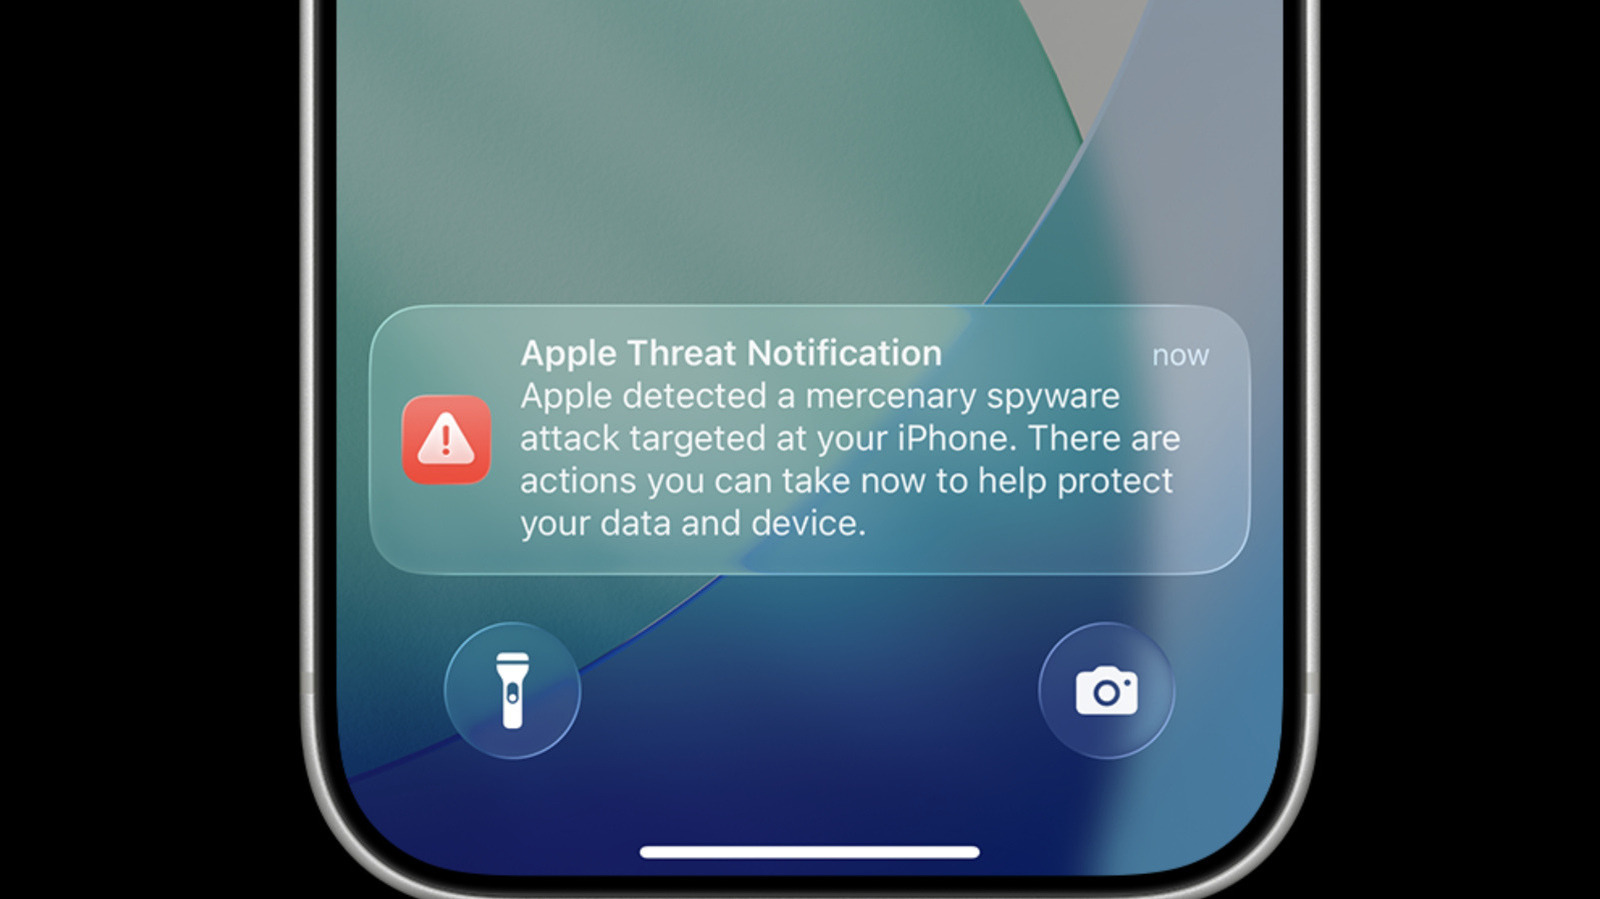
Apple has issued a new round of notifications to users identified as targets of mercenary spyware, such as Pegasus. The company confirmed to TechCrunch that it has updated the user experience for these warnings, aiming to make protective steps clearer for recipients. The fresh alerts were first reported on X by John Scott-Railton, a senior researcher at the University of Toronto’s Citizen Lab, on 13 August 2026.
The updated notification window explicitly informs users that there are immediate actions they can take to protect their data and devices. To support this, Apple has published a new dedicated support page detailing the nature of mercenary spyware and the specific steps users should follow if targeted. The company emphasises that these are high-confidence alerts indicating a user has been individually targeted, and they should be treated with serious urgency.
Mercenary spyware refers to sophisticated surveillance tools typically sold to state actors or governments. These tools are used to target specific individuals, including journalists, activists, politicians, and diplomats. Apple notes that while these attacks cost millions of dollars and are highly targeted, they are also difficult to detect and prevent. Consequently, the vast majority of users will never be targeted by such sophisticated threats.
Apple acknowledged that its investigations can never achieve absolute certainty regarding the detection of attacks. However, the company stated that notifications reflect activity on a device consistent with a mercenary spyware attack. It clarified that receiving a notification does not confirm that data has been compromised, but rather that suspicious activity consistent with an attack was detected.
To mitigate risk, Apple advises recipients to enable Lockdown Mode, an extreme protection setting that blocks most message attachments, FaceTime calls, invitations for Apple services, and shared photo albums. The company also recommends enlisting expert help, specifically pointing users to the Digital Security Helpline, a rapid-response emergency assistance service offered by the nonprofit Access Now.
Apple declined to disclose the specific methodology it uses to determine who is under attack, citing the need to prevent bad actors from using that information to evade detection in the future. The company continues to monitor for these threats, which remain a significant concern for high-value targets despite being rare for the general public.